Master Solutions Blog
Master Solutions has been serving the Naperville area since 1996, providing IT Support such as technical helpdesk support, computer support, and consulting to small and medium-sized businesses.
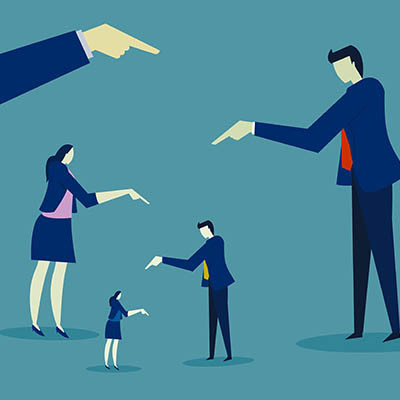
When a critical application goes down, your entire business grinds to a halt. You call your software provider, but they blame your internet connection. Your internet provider blames your hardware.
Before you know it, you are trapped in a frustrating cycle of finger-pointing, and your team still can’t get any work done. Let’s discuss how to break this cycle.
0 Comments
Vendor management is one of those corporate terms that sounds intentionally boring. In reality, it’s one of the most powerful ways to reclaim your time.
At its core, it means you have a single point of contact—us—to handle the relationships, the troubleshooting, and the procurement for every tech service you use.
Every business relies on vendors for a lot: software, services, you name it. They’re a huge part of our businesses’ ability to meet the market’s demands. The way business is done today, in order for them to do their job, they often need access to our data; but, just like you wouldn’t hand over your house keys to a stranger, you shouldn’t just hand over the keys to your data to every vendor without a second thought. When you give vendors broad, indiscriminate access, you're opening the door to some seriously bad situations.
You rely on your vendors to conduct business, but these vendors are just as susceptible to cyberattacks as your business is. How can you make sure you’re working with vendors who prioritize security? That’s what we’re covering in today’s blog.
Mobile? Grab this Article